Apple’s iPad may turn out to be more of a security risk than a useful tool for some, especially for those who, prior to yesterday’s launch, speculated that the iPad would be a God-send to the health care system, and possibly other sectors like businesses.
According to Steve, however, the iPad is designed primarily for the following activities:
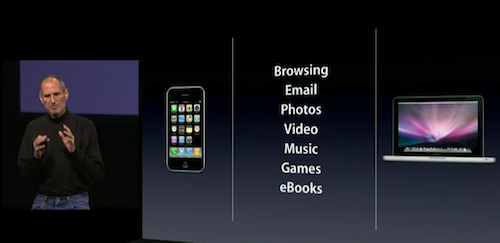
For some, even that may be something of a stretch.
As many have pointed out, the iPad is more of an oversized iPod Touch than an undersized MacBook Air, or as Daniel Tenner so aptly put it: “The uncomputer for the masses”.
When you send someone an email, you expect it to fall into the hands of its intended recipient, not someone who happened to get a hold of their device. I would never download all of my email onto an iPad because I can neither encrypt nor password protected it. Apple’s lockdown of the OS means third-party developers cannot intervene and remedy this situation because they’re not allowed to touch certain parts of the system.
Businesses and hospitals won’t be thrilled with employees and nurses running around with an easily swipeable device containing unprotected company secrets, client data, and patient information. Thanks to the “duplicating functionality” clause of the SDK TOS, developers can’t even write their own encrypted versions of Mail or the iWork suite.
If you want a secure iPad, you’ll either have to hope Apple implements it, or depend on each individual developer to properly secure their application’s data—a situation that nobody should be thrilled with.